
Overview
This guide introduces the IDMe OAuth 2.0 implementation and explains how partners can use it to access user data securely.
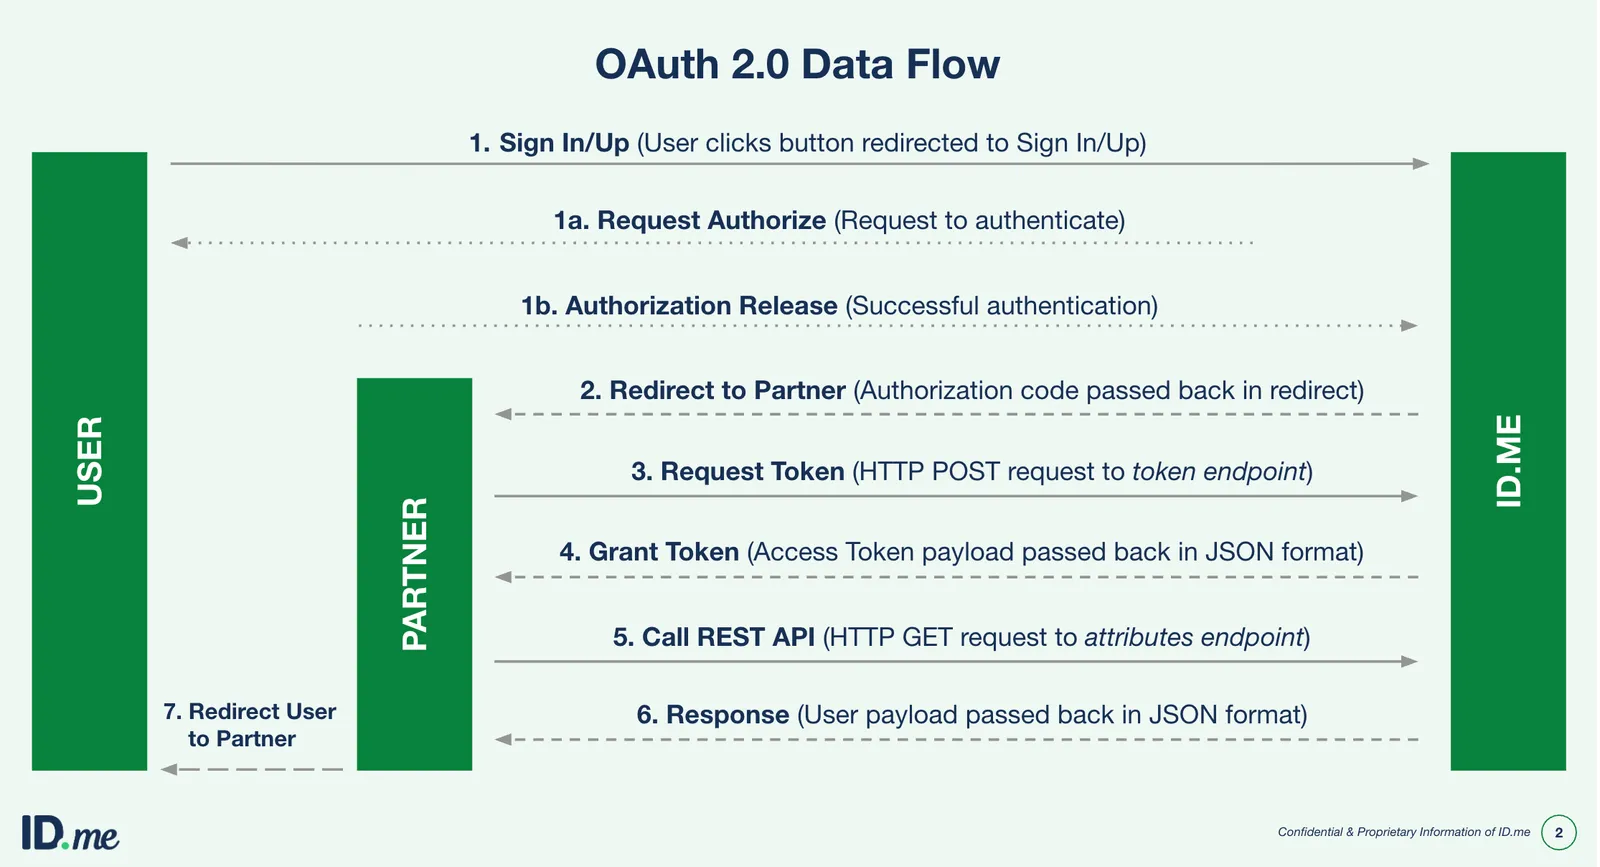
IDMe uses OAuth 2.0 RFC 6749 to authorize access to its APIs. To retrieve a user’s community data, your application must obtain an access_token. This token is user-specific, should be stored securely, and expires 5 minutes after issuance.
IDMe supports both full-page redirects and popup windows for the authorization flow. Once you’ve registered your application, you’ll find sample code, documentation, and the option to upload your company logo on the application details page.
IDMe supports Authorization Code Flow with PKCE (Proof Key for Code Exchange, RFC 7636). PKCE works with OAuth 2.0 Authorization Code Flow and is required by OAuth 2.1 guidance.